


Ethical Hacking is commonly known as Penetration Testing, a method used to assess the security of systems and networks. It is a security practice that involves testing a system or network to identify threats and vulnerabilities that could potentially be discovered and exploited by hackers, resulting in data loss, financial loss, and other damages. An Ethical Hacker carries out activities similar to those performed by criminal hackers, but does so legally with proper authorization from the relevant authorities. In simple language, ethical hacking is an authorized effort to gain unauthorized access to a computer system, application, or data in order to identify potential security weaknesses.
The Role of Ethical Hacking in Cybersecurity
- Protect Digital Assets: Ethical hacking helps safeguard valuable data and digital assets from potential cyber threats and unauthorized access.
- Find and Fix Vulnerabilities: It helps identify weaknesses in systems and networks so they can be addressed before they are exploited by attackers.
- Maintain Compliance: Ethical hacking helps organizations follow relevant industry standards, security guidelines, and regulatory requirements.
- Strengthen Cybersecurity: By uncovering security gaps, ethical hacking helps improve an organization’s overall cybersecurity and build stronger defences against attacks.
- Build Career Opportunities: Ethical hacking opens up promising career opportunities for aspiring cybersecurity professionals, along with strong potential for career growth.
Why Choose Ethical Hacking as a Career?


Understand
Corporate Data Breaches

Grow
Professionally


Course Duration
40 hours - 2 classes per week

Eligibility Criteria
- Applicants should have basic knowledge of databases, server-side programming such as PHP, JSP, or ASP.NET, along with fundamental networking knowledge.
- If you do not have the required background knowledge, you can first complete our “INDUSTRY READY” Course to meet the eligibility requirements

Course Fees
Classroom Training
Rs.14,500/-
Inclusive of all applicable taxes
Online Training
Rs.24,500/-
Rs.14,500/-
Inclusive of all applicable taxes
What Can You Expect from the Course?
40 Hours of In-Depth Training
delivered by experienced cybersecurity experts
Comprehensive Study Materials
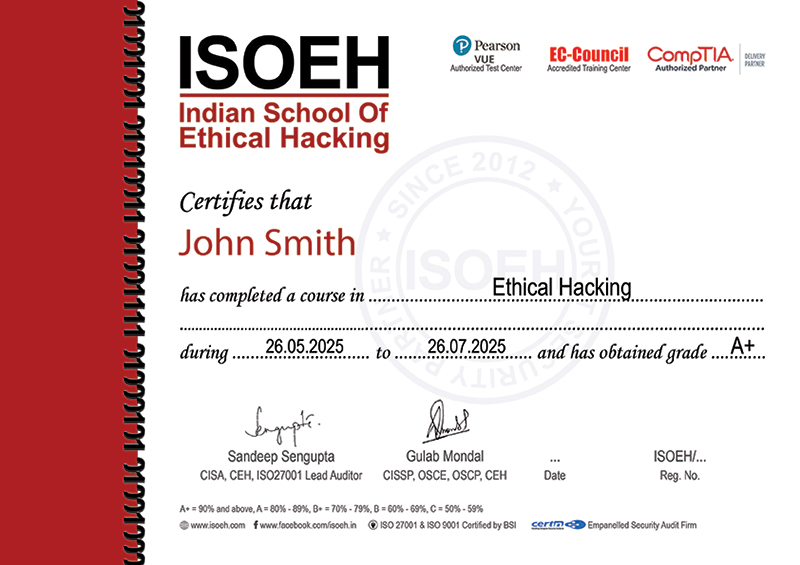
Ethical Hacking Certification
Earn a Certificate of Completion in Ethical Hacking after successfully completing the examination, along with alumni status.
Course Completion Certificate Example
Benefits of Learning Ethical Hacking
- Develop comprehensive knowledge of different cybersecurity threats and the risks they pose.
- Get practical, hands-on experience under the guidance of industry experts using advanced cybersecurity tools.
- Get the opportunity to work with the high-end laboratory facilities of the audit firm.
- Earn a certification that can strengthen your job prospects and professional credibility.
- Develop skills that enable you to contribute to strengthening cybersecurity on a global level.
- Explore rewarding career opportunities with the potential for high-paying jobs in cybersecurity.
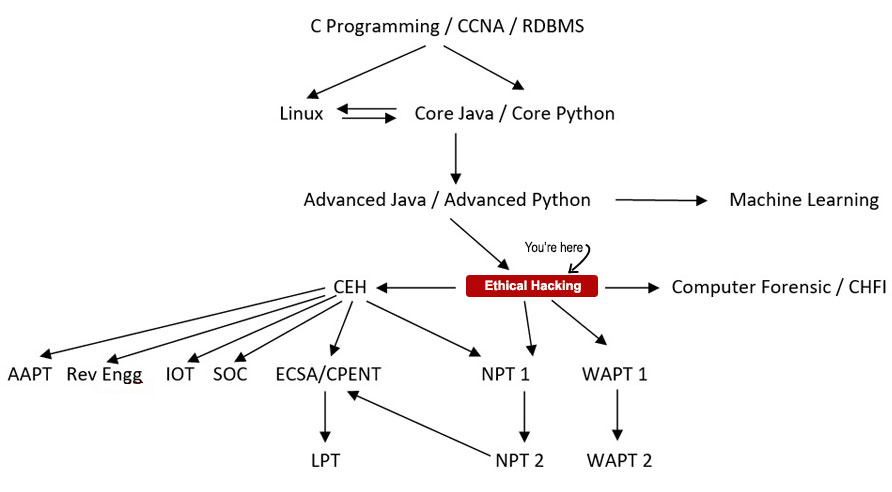
Roadmap to be an Ethical Hacker
Course Details
- Complete 40 hours of training through weekly 2-hour classes designed for structured learning.
- Enroll in the classroom or online training programme at a course fee of Rs. 14,500/- for either mode.
- Learn through a combination of theoretical concepts and practical application for a more comprehensive understanding.
- What is Ethical Hacking (Day 1)
- What are the different types of hackers (Day 1)
- Five phases of hacking (Day 1)
- Scope of Ethical Hacking (Day 1)
- Passive Information Gathering (Day 2)
- Active Information Gathering (Day 2)
- Foot-Printing (Day 2)
- OSINT (Day 2)
- Port Scanning (Day 3)
- Network Sweeping (Day 3)
- Vulnerability Scanning (Day 3)
- Service Version Detection (Day 3)
- OS Fingerprinting (Day 3)
- Introduction to Metasploit Framework (Day 4)
- Introduction to Exploits & Payloads (Day 4)
- Type of Connections (Day 4)
- Exploit MS17-010 Vulnerability (Day 4)
- Introduction to Privilege Escalation (Day 5)
- Types of Privilege Escalation (Day 5)
- Bypassuac and getsystem (Day 5)
- Android Hacking (Day 6)
- Software based vulnerabilities (Day 6)
- Introduction to Active Directory Components (Day 7)
- LDAP in Active Directory (Day 7)
- Active Directory Functionality (Day 7)
- Service Principal Name (SPN) (Day 7)
- Kerberos Basics and Overview (Day 8)
- Components of Kerberos (KDC, Ticket Granting Ticket, etc.) (Day 8)
- Kerberos Authentication Process (Day 8)
- Kerberos Tickets and Encryption (Day 8)
- Introduction to Kerberos Attacks (Day 8)
- Introduction to Malware (Day 9)
- Types of Malwares (Viruses, Worms, Trojans, etc.) (Day 9)
- Malware Analysis Techniques (Day 9)
- Common Malware Distribution Methods (Day 9)
- Malware Detection and Prevention (Day 9)
- Introduction to Network Sniffing (Day 10)
- Passive vs. Active Sniffing (Day 10)
- Common Network Sniffing Tools (Day 10)
- Man-in-the-Middle (MITM) Attacks and Techniques (Day 10)
- Introduction to Cryptography (Day 11)
- Symmetric vs. Asymmetric Encryption (Day 11)
- Common Cryptographic Algorithms (e.g., AES, RSA) (Day 11)
- Steganography Techniques and Applications (Day 11)
- Introduction to Wireless Networks (Day 12)
- Types of Wireless Security Protocols (e.g., WEP, WPA, WPA2) (Day 12)
- Wireless Network Scanning and Enumeration (Day 12)
- Exploiting Wireless Vulnerabilities (Day 12)
- Introduction to Website Attacks (Day 13)
- How Website Attacks Work (Day 13)
- Types of Vulnerabilities Exploited (Day 13)
- Enumeration Techniques (Day 13)
- Introduction to Cross-Site Scripting (XSS) (Day 14)
- Understanding How XSS Works (Day 14)
- Types of XSS Attacks (Reflected XSS, Stored XSS, DOM-based XSS) (Day 14)
- Techniques for Detecting and Exploiting XSS Vulnerabilities (Day 14)
- Introduction to SQL Injection (SQLi) (Day 15)
- Mechanism of SQL Injection (Day 15)
- Common Types of SQL Injection Attacks (Union-Based, Blind SQLi, Error-Based) (Day 15)
- Techniques for Exploiting SQL Injection Vulnerabilities (Day 15)
- Introduction to Cross-Site Request Forgery (CSRF) (Day 16)
- How CSRF Attacks Work (Day 16)
- Examples of CSRF Exploitation (Day 16)
- Prevention and Mitigation Strategies (Day 16)
- Understanding Cookie Stealing and Session Hijacking (Day 17)
- Techniques for Cookie Stealing and Session Hijacking (Day 17)
- Data Tampering Attacks on Websites (Day 17)
- Phishing Attacks: Methods and Impacts (Day 17)
- File Upload Vulnerabilities: Risks and Exploitation (Day 17)
- Introduction to IoT Security (Day 18)
- IoT Device Identification and Enumeration (Day 18)
- Exploiting IoT Communication Protocols (Day 18)
- Webcam Attacks on IoT Devices (Day 18)
- Introduction to DDoS Attacks (Day 19)
- Types of DDoS Attacks (Day 19)
- DDoS Attack Techniques (Day 19)
- Cloud Security Fundamentals (Day 19)
- Introduction to IDS/IPS (Day 20)
- Types of IDS (Network-based, Host-based) (Day 20)
- Types of IPS (Network-based, Host-based) (Day 20)
- Honeypots (Day 20)
Hacking Tutorials
Read All Tutorials »
Building a career in Digital Forensics - How promising is the future? A thorough career guide
Read Details »Hacking Videos
Explore All Videos »How to Hiding Your Secret File using Steganography?
View On Youtube »Enroll Now
Fields marked with * are mandatory.
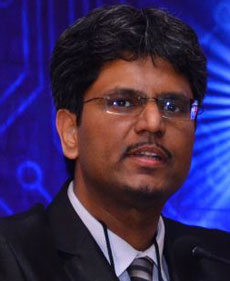
With over 27 years of experience in Information Technology and Cyber Security, Mr. Sandeep Sengupta has made significant contributions to the field, providing solutions across India and internationally, including Singapore (2009-2010) and New Zealand (2002-2003). He is a certified lead auditor for standards such as ISO 27001 (Information Security), ISO 22301 (Business Continuity), ISO 9001 (Quality Management), and ISO 27701 (Data Protection & Privacy/GDPR). Additionally, he holds certifications as a Certified Ethical Hacker (CEH) and a Certified Information Systems Auditor (CISA).
Mr. Sengupta has conducted audits for organizations such as PwC, KPMG, Tata Steel, SAIL, Capgemini, Genpact, ITC, Airtel, Vodafone, ONGC, National Power Grid, Bandhan Bank, PayU, Vedanta, and Accenture, among others. He collaborates with law enforcement agencies, including the CID and Lal Bazar Police Cyber Cell, on cybercrime investigations.
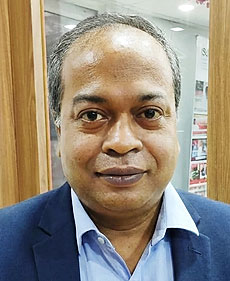
Mr. Saumitra Biswas is M.Tech in computer science from Netaji Subhash Engineering College, GATE qualified in computer science and a MSC in statistics from Kalyani University. He has 20 years of experience. His technical interests include Machine Learning, Neural Networks, Genetic Algorithms and Object Oriented Programming. He is skilled in C, C++, C#, Dotnet, Java, Python, Matlab, Unix, MS Windows XP, Windows 7, My SQL, Oracle, MS Access, HTML, XML, CSS and PHP. He take classes on AI & ML in ISOAH, as well as act as mentors to interns & project trainees.
Ratings & Reviews
Course: Python Programming & Ethical Hacking
I have started my journey as a student of ISOAH since 2021! In my opinion, if someone wants to start his or her career in cybersecurity then ISOAH is one of the best places. This institute not only provides courses to students rather they also helps to make a proper career for every student in the field of Cyber Security with proper direction and guidance. The mentors and faculties are very helpful and they are always there for help! I feel proud to be a student of ISOAH.
Course: Ethical Hacking
It is quite true to say that I was a student of English (Hons) before when I came to know about this course which made me feel so interested and alluring. Throughout the journey of CEH (Ethical Hacking) at the Indian School of Ethical Hacking, I would like to say that my respected mentors and fellow mates at this institute helped me a lot in chasing my goal and provided me a widespread information about technology which was the sole reason of cracked such a very tough and hard global CEH exam. Thank you very much to ISOEH for all of my endeavours.
Course: CCNA & Ethical Hacking
ISOEH has ignited my passion for cybersecurity with its fascinating courses. The dynamic curriculum, led by industry experts, offers a perfect blend of theory and hands-on experience. The engaging classes and real-world simulations have made learning cybersecurity not just educational but enjoyable. ISOEH's commitment to ethical hacking adds a valuable dimension to the training, ensuring graduates are not only skilled but also responsible professionals. In just a short time, ISOEH has opened my eyes to the captivating world of cybersecurity.
Course: CCNA & Ethical Hacking
I joined ISOEH for CCNA and an Ethical hacking course while continuing with my B.Sc in Computer Science at KIIT UNIVERSITY. The training at ISOEH was hands-on practical learning based. And the mentoring I received from their faculty members was a light to accomplish my goals. The Indian School of Ethical hacking is the golden treasure of knowledge, a weapon to face your tomorrow.

Course: Ethical Hacking (Non Global)
Isoeh is the good institute I have learn knowledge about ethical hacking. This institute very good to learn and practise about hacking. Sir Sombed has given very good knowledge about ethical hacking.
Course: Ethical Hacking (Non Global)
It's a good institute I had gained lots of knowledge I had an experience in ethical hacking and it's institute faculty is good they are frankly with students I am a lucky that I have training in this institute.
Course: Ethical Hacking (Non Global)
Somdeb sir was good and gave me very good knowledge about ethical hacking.....if I am going to do advance in ethical hacking I will be looking for him...
Course: Ethical Hacking (Non Global)
Excellent Place to learn CCNA and Ethical Hacking. Best institute to learn on networking and Hacking. Lucky to be a part of this Institution.. Teachers and Faculties are very helpful and always ready to help. They got huge knowledge on every subject and every topic. I was under Subhendu Sir from very 1st day, he is too good and has good expertise and knowledge in his domain of Networking and also completed the course under him. For EH I was under Sanchayan Sir and Anubhav Sir they were also too good in teaching Hacking and its tools and how it works and cleared all my doubt. On other hand Kundan Sir also helped me with all my problems which I was facing and also help me to get rid from all my problems so I will be thankful to ISOEH for life. It was a good journey for me in learning and gathering knowledge and looking forward to do more courses from here and will also suggest my friend about this Institution. Thank You.
Career Opportunities & Job Prospects
Cybersecurity and networking have emerged as promising fields, offering growing employment opportunities for ethical hackers. Ethical hackers can pursue roles as cybersecurity professionals across both government and private-sector organizations. Apart from IT companies, ethical hackers are also in demand across sectors such as financial services, airlines, retail, and hospitality. Government departments, including military and law-enforcement agencies, along with defence organizations, forensic laboratories, detective firms, and investigative services, also offer career opportunities for ethical hackers. Experienced ethical hackers may also find opportunities with investigative agencies such as the Central Bureau of Investigation, the National Security Agency, and the Federal Bureau of Investigation. While some large organizations maintain in-house security testing teams, others hire external professionals or contractors to assess and audit their systems. Freshers may begin their careers with an internship before moving into a full-time position, with starting salaries of around ₹2.5 lakh per annum. With around one year of professional experience, an individual may earn up to ₹4.5 lakh per annum. Professionals with five or more years of experience can potentially earn between ₹10–12 lakh per annum.
FAQs
- Introduction to Ethical Hacking
- Legality and Ethics
- Networking & Basics
- Foot Printing
- Google Hacking
- Scanning
- Enumeration
- System Hacking
- Windows Hacking
- Trojans & Backdoors
- Virus & Worms
- Sniffers
- Social Engineering
- Proxy Server & Packet Filtering
- Denial of Service Attack
- Phishing
- Session Hijacking
- Penetration Testing
- Vulnerability Assessment
- Linux Hacking
- Physical Security
- Hacking Web servers
- Web Application Vulnerabilities
- Web Based password Cracking Techniques
- SQL Injection Vulnerabilities
- Cryptography
- Wireless Network Hacking and Countermeasures
- Evading IDS, Firewalls and Detecting Honey Pots
- Buffer Overflows
- Reverse Engineering
- Hacking Database Servers
- Steganography
- Spying Technologies
- Hacking Routers and Firewalls
- Computer Forensics and Incident Handling
- Botnets
- Hacking emails
- Privacy on the Internet
- Creating Security Policies
- Exploit Writing
- Patch Management
- Covering Tracks
The course consists of 40 hours of training, with two classes conducted each week.
The course combines both theoretical concepts and practical training to provide a balanced learning experience.
Participants should have basic knowledge of databases, server-side programming such as PHP, JSP, or ASP.NET, along with fundamental networking knowledge.
The top organizations like such as Infosys, Wipro, TCS, Tech Mahindra, IBM etc. are seeking good ethical hackers. The profiles that are on offer include Security Executive, Web Security Manager/Administrator, Network Security Administrator, Network Security Systems Manager and much more.
You can pursue advanced courses such as NPT, WAPT, AAPT, iOS Application Penetration Testing, and other related programmes after completing this course.
Course Fees
Rs.24,500/-Rs.14,500/-
Inclusive of all taxes
Batches
Weekday Batches for Bhubaneswar Center:
Oct, 2026
Oct, 2026
Jan, 2027
Weekday Batches for Kolkata Center:
Oct, 2026
Oct, 2026
Dec, 2026
Weekend Batches for Kolkata Center:
Oct, 2026
Oct, 2026
Dec, 2026
Member of: